Our Services
Network Architecture
Enterprise-grade structured cabling, managed switch deployment, VLAN segmentation, and complete network architecture designed for businesses that depend on reliable, fast, and secure connectivity across every floor and every device.
Learn more →Network Security
Comprehensive network hardening and threat protection for businesses — next-generation firewalls, intrusion detection and prevention, network segmentation, and continuous monitoring that keeps your business safe from external threats and internal vulnerabilities.
Learn more →Data Backup
Automated, verified, and encrypted backup systems that protect your business data across on-premise servers, cloud applications, and workstations — so when hardware fails, ransomware strikes, or someone deletes the wrong file, recovery is fast, complete, and stress-free.
Learn more →Data Recovery
Professional data recovery from failed hard drives, corrupted file systems, accidental deletion, and damaged storage media — fast, confidential, and thorough, with a priority on getting your business back to operational as quickly as possible.
Learn more →Data Disaster Recovery
Business continuity and disaster recovery planning that keeps your operations running when the worst happens — comprehensive DR plans, failover systems, RPO/RTO optimization, and regular testing so your recovery works when it matters most.
Learn more →Cyber Security
End-to-end cyber security for businesses — endpoint protection, SIEM monitoring, vulnerability assessments, penetration testing, compliance support (SOC 2, ISO 27001, PIPEDA, PHIPA), and incident response that protects your data, your reputation, and your bottom line.
Learn more →Access Control Management
Physical and digital access control management — credential lifecycle management, role-based access policies, identity management, audit trails, and compliance reporting that ensures the right people have the right access to the right systems at the right time.
Learn more →Remote Data Access and Sharing
Secure VPN, remote desktop, and cloud-based access solutions that let your team work from anywhere without compromising security — zero-trust architecture, encrypted connections, and seamless access to files, applications, and systems from any device, any location.
Learn more →Secure Email
Enterprise-grade email security — encrypted email infrastructure, anti-phishing protection, email security gateways, SPF/DKIM/DMARC configuration, and compliance-ready email management that protects your business from the most common attack vector in cyber crime.
Learn more →IT Access Control Management Services Toronto
Physical and digital access control management — credential lifecycle management, role-based access policies, identity management, audit trails, and compliance reporting that ensures the right people have the right access to the right systems at the right time.
Free consultation with a YuranTech expert
Access Control Management — YuranTech
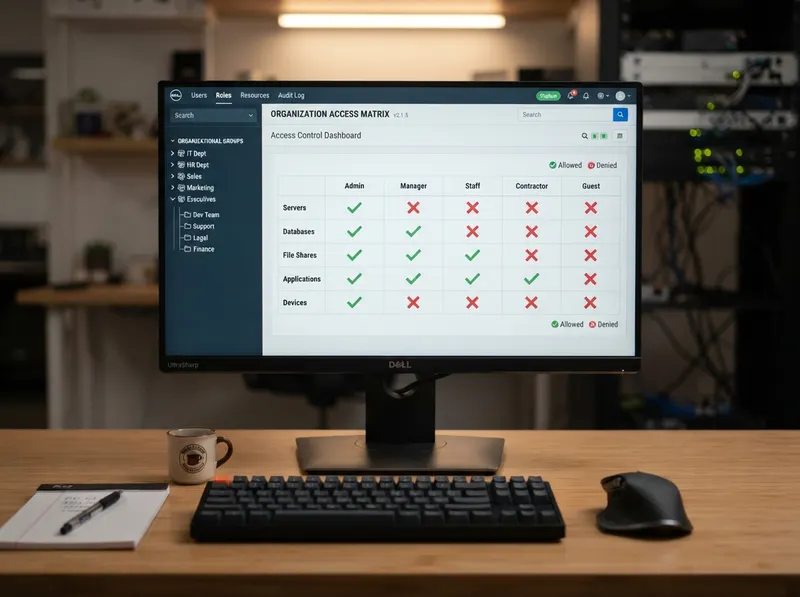
Access control is where physical security meets digital security. Who can open which door? Who can log into which system? Who can access which files? These questions seem simple, but in a growing business with employees joining, changing roles, and leaving regularly, managing access becomes one of the most important — and most neglected — security disciplines. Stale credentials, over-provisioned accounts, shared passwords, and absent audit trails are the vulnerabilities that attackers exploit most often, because they are the easiest to find and the hardest for businesses to track. YuranTech provides access control management services that cover both the physical and digital sides of access — building entry systems, network credentials, application accounts, cloud service permissions, and file-level access — managed through a unified framework that ensures consistency, auditability, and compliance across your entire organization. On the physical side, we manage building access control systems — card readers, fob systems, biometric readers, and mobile credential platforms — including day-to-day credential provisioning, access level changes, and revocation when employees leave. We design role-based access templates so new employees receive the correct door access, elevator permissions, and time-based restrictions automatically based on their role, department, and location. Building access event logs are maintained and available for audit. On the digital side, we implement identity and access management (IAM) practices across your IT environment. We configure Active Directory, Azure AD, or cloud identity providers with role-based access control (RBAC) policies that grant users access to the applications, file shares, and cloud services their role requires — and nothing more. The principle of least privilege is the foundation: every user has the minimum access necessary to do their job. When an employee changes roles, their access profile is updated. When an employee leaves, their credentials — all of them, across every system — are revoked within hours, not weeks. Multi-factor authentication (MFA) is implemented across all remote access, cloud services, and administrative accounts to ensure that stolen passwords alone cannot grant access. We also deploy privileged access management (PAM) for administrative accounts that control critical infrastructure — domain admin, firewall admin, database admin — with session logging, just-in-time elevation, and approval workflows that prevent these powerful credentials from being used without oversight. Audit trails and compliance reporting tie everything together. We maintain complete logs of who accessed what, when, and from where — across both physical and digital systems — and produce compliance-ready reports for SOC 2, ISO 27001, PIPEDA, PHIPA, and other frameworks. When your auditor asks for evidence that access controls are in place and operating effectively, we provide it without scrambling. Integration with network security, cyber security, and secure email ensures that access control is part of your complete security posture — not a standalone system operating in isolation.
What Access Control Management Includes
Every access control management engagement covers both physical and digital access across your entire organization:
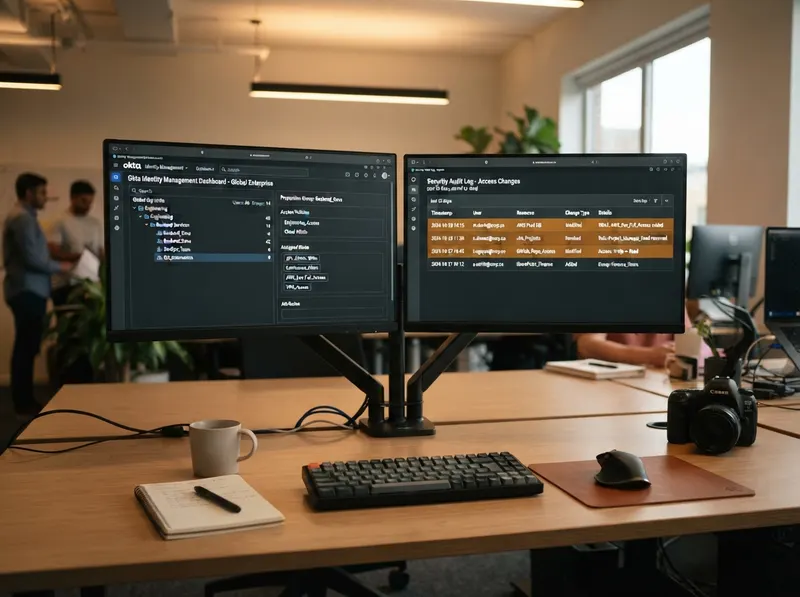
- Physical access system management: credential provisioning, modification, and revocation
- Role-based access templates for physical building entry systems
- Identity and access management (IAM) configuration: Active Directory, Azure AD, cloud identity
- Role-based access control (RBAC) policy design and enforcement
- Multi-factor authentication (MFA) deployment across all access points
- Privileged access management (PAM) for administrative credentials
- Automated onboarding and offboarding access workflows
- Complete audit trail logging for physical and digital access events
- Compliance reporting for SOC 2, ISO 27001, PIPEDA, PHIPA
- Quarterly access reviews and permission audits
The result is an access control program where every credential is managed, every permission is justified, every access event is logged, and every departure triggers immediate revocation — so your business is protected from both external threats and internal over-provisioning.
Our Approach to Access Control Management
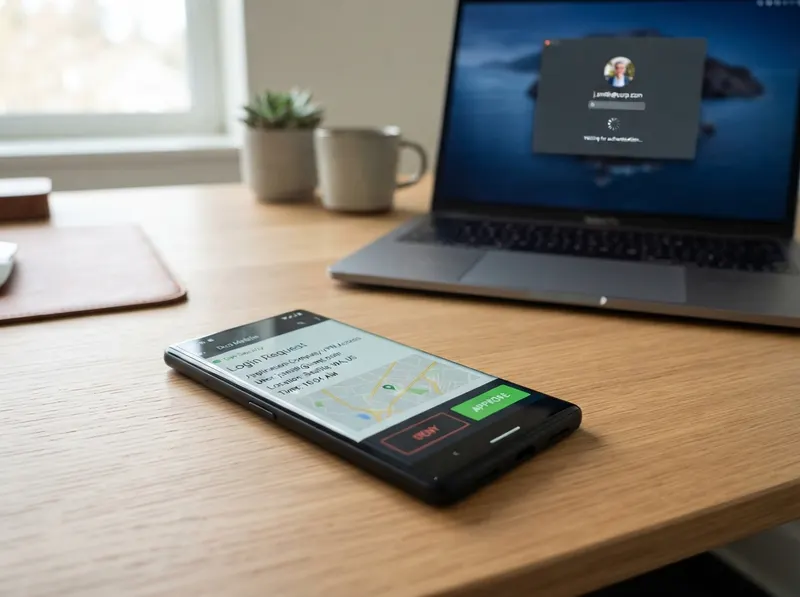
Most access control problems start with good intentions and no process. An employee needs access to a new system, so IT grants it. The employee changes roles, but nobody updates their access. Another employee leaves, and their Active Directory account is disabled but their cloud service logins, VPN credentials, and building fob remain active for months. Over time, access creep means most users have far more permissions than their role requires, and departed employees still have active credentials in systems no one remembers to check. We fix this by implementing a structured access management framework: role-based templates that define what each job function needs, automated provisioning and deprovisioning workflows that trigger on HR events, quarterly access reviews where managers verify their team members' permissions, and privileged access management for administrative accounts. The goal is a system where access is granted by policy, not by ad-hoc request, and revoked automatically, not when someone eventually remembers.
Identity & Access Technology
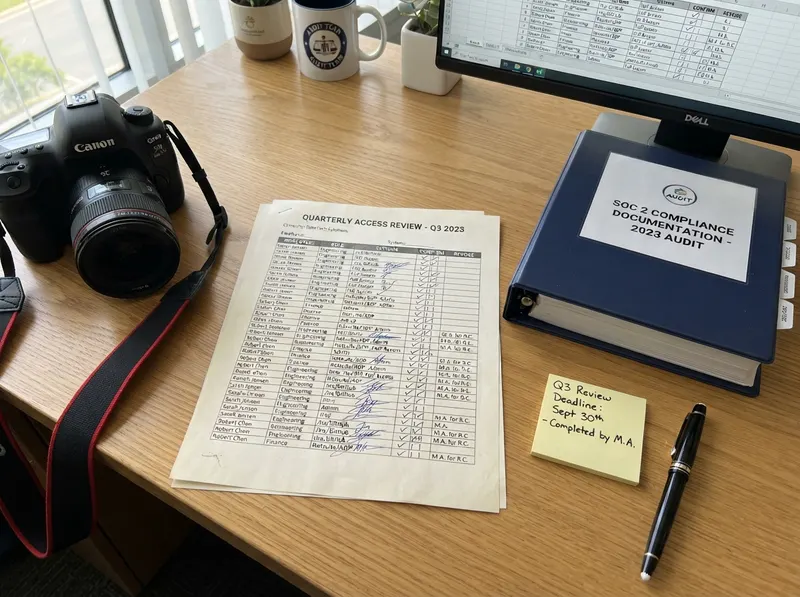
Our access control management platform integrates with your existing identity infrastructure — Active Directory, Azure AD, Okta, Google Workspace — and extends it with structured RBAC policies, automated lifecycle management, and comprehensive audit logging. MFA is deployed using standards-based protocols (TOTP, FIDO2, push notification) that work across VPN, cloud applications, email, and administrative consoles. Privileged access management implements just-in-time elevation, session recording, and approval workflows for administrative credentials — ensuring that high-privilege access is monitored and auditable. For physical access, we integrate with building access control hardware to synchronize credential management with HR systems — new hire event in HR triggers door access provisioning; termination event triggers credential revocation across both physical and digital systems. Compliance reporting is automated: role-based access matrices, access review certifications, and audit trail exports are available on demand in formats compatible with SOC 2, ISO 27001, and PIPEDA audit requirements. Integration with cyber security provides correlation between access events and security incidents.
Business-First Approach
We start with your business operations and design technology around them — not the other way around. Every recommendation is tied to a business outcome: uptime, security, productivity, or compliance.
Full-Stack IT Coverage
Network, security, backup, disaster recovery, email, access control, and remote access — all managed by one team. Integrated security that works because the systems are designed together, not bolted together.
Toronto & GTA Expertise
We serve businesses across Toronto, Mississauga, Vaughan, Markham, and the surrounding GTA. Local presence means fast on-site response when you need it and an understanding of the regulatory environment that affects your business.
Proactive, Not Reactive
We monitor, patch, and harden your systems continuously — not just when something breaks. Proactive management means fewer incidents, less downtime, and predictable IT costs instead of emergency repair bills.
Need access control management? Let's design your solution.
Free consultation with a YuranTech expert
Common Questions
Access Control Management FAQ
Answers to the questions business owners ask most about access control management.
Least privilege means every user has the minimum access necessary to perform their job — and no more. If an accountant needs access to the financial system and shared drives for the finance team, that is what they get. They do not get access to the engineering file share, the HR system, or the IT admin console. This limits the damage if any single account is compromised.
Start Your Access Control Management Project
Tell us a little about your business and your access control management needs and we'll reach out with a tailored proposal.
Our Other Services
Network Architecture
Enterprise-grade structured cabling, managed switch deployment, VLAN segmentation, and complete network architecture designed for businesses that depend on reliable, fast, and secure connectivity across every floor and every device.
Learn more →
Network Security
Comprehensive network hardening and threat protection for businesses — next-generation firewalls, intrusion detection and prevention, network segmentation, and continuous monitoring that keeps your business safe from external threats and internal vulnerabilities.
Learn more →
Data Backup
Automated, verified, and encrypted backup systems that protect your business data across on-premise servers, cloud applications, and workstations — so when hardware fails, ransomware strikes, or someone deletes the wrong file, recovery is fast, complete, and stress-free.
Learn more →
Data Recovery
Professional data recovery from failed hard drives, corrupted file systems, accidental deletion, and damaged storage media — fast, confidential, and thorough, with a priority on getting your business back to operational as quickly as possible.
Learn more →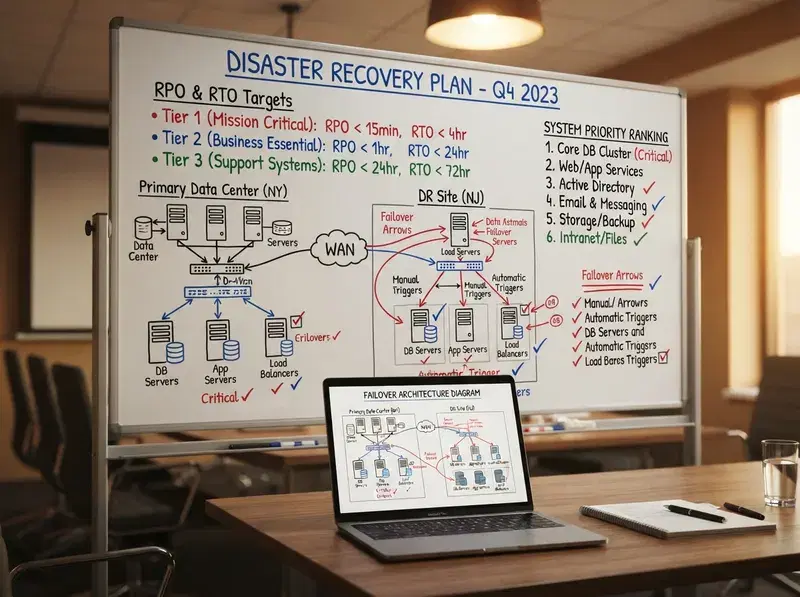
Data Disaster Recovery
Business continuity and disaster recovery planning that keeps your operations running when the worst happens — comprehensive DR plans, failover systems, RPO/RTO optimization, and regular testing so your recovery works when it matters most.
Learn more →
Cyber Security
End-to-end cyber security for businesses — endpoint protection, SIEM monitoring, vulnerability assessments, penetration testing, compliance support (SOC 2, ISO 27001, PIPEDA, PHIPA), and incident response that protects your data, your reputation, and your bottom line.
Learn more →
Remote Data Access and Sharing
Secure VPN, remote desktop, and cloud-based access solutions that let your team work from anywhere without compromising security — zero-trust architecture, encrypted connections, and seamless access to files, applications, and systems from any device, any location.
Learn more →
Secure Email
Enterprise-grade email security — encrypted email infrastructure, anti-phishing protection, email security gateways, SPF/DKIM/DMARC configuration, and compliance-ready email management that protects your business from the most common attack vector in cyber crime.
Learn more →